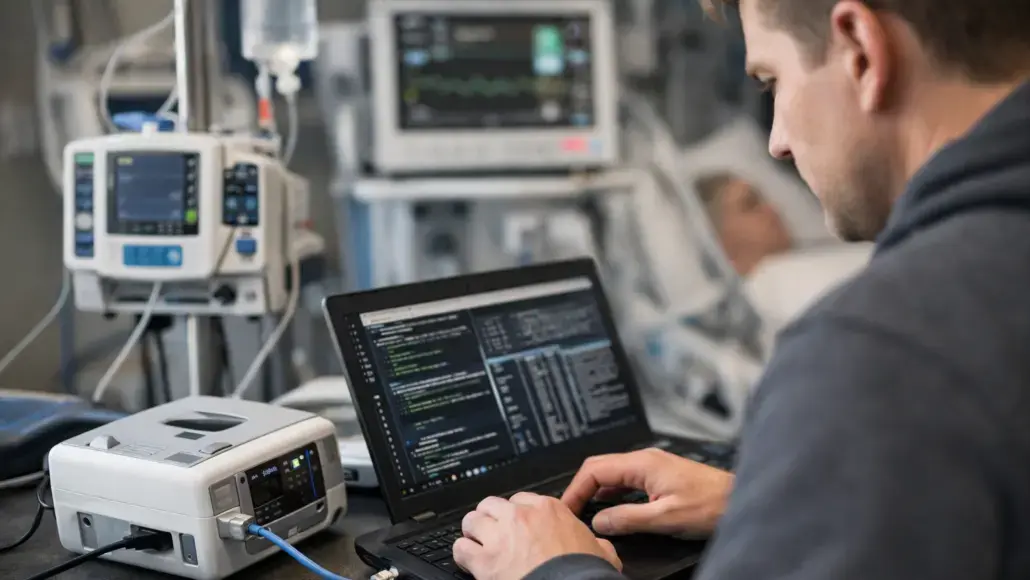

A medical device can be a remarkably sophisticated piece of technology. Modern devices may connect to hospital networks, communicate with cloud platforms, exchange data with mobile applications, receive software updates remotely, and interact with other clinical systems. That connectivity creates valuable capabilities for clinicians and patients, but it also creates cybersecurity risks that traditional IT security testing does not always address adequately. A vulnerability in an ordinary business application may expose files or disrupt an internal service. A vulnerability in a medical device can potentially affect patient data, clinical workflows, device availability, or even the delivery of care.
This is why penetration testing for medical devices requires a different mindset from conventional IT security testing. The objective is not simply to determine whether a system can be compromised. Testers must understand the device’s intended clinical function, operational environment, safety considerations, regulatory expectations, communication protocols, and potential consequences of exploitation. Organizations such as the U.S. Food and Drug Administration (FDA) have increasingly emphasized cybersecurity throughout the medical device lifecycle, making security testing an important component of responsible device development and risk management.
Medical Devices Operate in a Safety-Critical Environment
Traditional IT penetration testing typically focuses on systems such as web applications, databases, servers, cloud environments, endpoints, and corporate networks. Testers commonly assess whether they can gain unauthorized access, escalate privileges, extract sensitive information, or move laterally through an environment. These objectives remain relevant to connected medical devices, but they do not capture the full range of risks involved when technology is directly or indirectly involved in patient care.
A medical device may have a specific clinical purpose that must continue functioning safely even when cybersecurity testing is underway. For example, a connected monitoring system may collect and transmit physiological information, while an infusion pump may control medication delivery. An exploitation technique that merely causes downtime in a corporate application could have significantly different implications when applied to clinical equipment. Testers therefore need to consider confidentiality, integrity, and availability alongside patient safety and the device’s intended performance.
The surrounding environment also makes medical device testing more complicated. A device may communicate with hospital information systems, electronic health records, diagnostic equipment, wireless networks, vendor platforms, or cloud services. Some devices may run outdated operating systems or contain legacy components because replacing or modifying them could affect regulatory status, compatibility, or validated functionality. A penetration test must account for these dependencies rather than treating the device as an isolated computer.
The Testing Methodology Must Account for Device-Specific Risks
One of the most important differences between medical device penetration testing and conventional IT testing is the need to understand how the device actually works. Before testing begins, security professionals need a clear picture of the device architecture, software components, communication interfaces, authentication mechanisms, update processes, external dependencies, and intended use. Threat modeling and architectural analysis can help identify where an attacker might enter the system and what could happen if a particular component were compromised.
Testing may include assessment of network services, APIs, wireless interfaces, mobile applications, cloud connections, authentication controls, encryption, firmware, update mechanisms, exposed ports, and other attack surfaces. However, the techniques must be selected carefully. Aggressive scanning, fuzzing, malformed input, or exploitation could interfere with device functionality if performed without appropriate safeguards. Testing in a controlled environment or using a representative test device is often preferable when production equipment cannot safely withstand intrusive techniques.
Another important distinction is that medical device security testing should consider both technical vulnerabilities and their potential clinical consequences. A tester might identify a vulnerability that allows unauthorized modification of device settings. In a conventional IT report, that could be described primarily as an integrity issue. For a medical device, the analysis may need to go further by determining whether manipulation could alter a clinical function, create misleading information, interfere with alarms, or otherwise affect patient care. This context helps security teams prioritize remediation based on actual risk rather than technical severity alone.
Regulatory Expectations Add Another Layer to Security Testing
Medical device manufacturers operate within a regulatory environment that makes cybersecurity more than an optional technical exercise. In the United States, the FDA has incorporated cybersecurity considerations into its expectations for medical device manufacturers, including requirements and guidance related to cybersecurity risk management and the design of connected devices. The regulatory emphasis reflects a broader industry understanding that cybersecurity should be addressed throughout development rather than treated solely as a post-release problem.
For manufacturers, testing therefore needs to fit into a broader security lifecycle. Penetration testing can provide evidence that security controls have been challenged under realistic conditions, but it should complement activities such as threat modeling, vulnerability assessment, secure software development, security architecture review, code analysis, and risk assessment. A penetration test performed immediately before launch cannot compensate for security weaknesses that were overlooked during design.
This is where FDA-compliant penetration testing can become an important consideration for manufacturers seeking a structured approach to evaluating device security. Compliance should not be interpreted as a simple certification that a device is “secure.” Rather, testing should be aligned with applicable regulatory expectations, documented appropriately, and integrated into the manufacturer’s overall cybersecurity risk-management process. The precise testing approach will depend on the device, its architecture, intended use, threat model, and applicable regulatory requirements.
Testers Must Balance Thoroughness With Patient Safety
A penetration test against a corporate website can often involve aggressive techniques with relatively limited consequences if the system becomes temporarily unavailable. Medical devices require more caution because unexpected behavior may have safety implications. The testing team must establish clear boundaries before attempting potentially disruptive activities and should understand how to stop or reverse a test if unexpected behavior occurs.
This does not mean medical device penetration testing should be superficial. In fact, meaningful testing can require highly technical analysis. Researchers may examine firmware, reverse engineer components, inspect communication protocols, analyze authentication mechanisms, evaluate update systems, and test whether unauthorized users can manipulate sensitive functionality. The difference lies in how these techniques are controlled and interpreted.
A strong testing program also establishes an appropriate test environment. Where practical, manufacturers can provide dedicated devices, representative configurations, isolated networks, test accounts, simulated clinical data, and documented recovery procedures. These precautions allow testers to explore realistic attack scenarios while reducing the possibility of disrupting patient care or compromising sensitive information. Clear rules of engagement are especially important when third-party systems, hospitals, connected devices, or cloud services are involved.
Medical Device Testing Looks Beyond the Device Itself
Another major difference is the importance of the device ecosystem. A medical device may be secure in isolation while still creating risks through the systems surrounding it. Consider a device that communicates with a mobile application and a cloud service. An attacker might target the application rather than the hardware, compromise credentials through an exposed API, or manipulate communications between components. Testing therefore needs to examine trust relationships and data flows across the complete ecosystem.
Supply-chain considerations can also influence the assessment. Medical devices frequently incorporate third-party software, open-source libraries, operating system components, hardware modules, and external services. A vulnerability in one dependency may create exposure even when the manufacturer’s proprietary code is well protected. Software composition analysis, vulnerability management, and supplier security assessments can complement penetration testing by identifying weaknesses that may not be discovered through hands-on exploitation alone.
The same principle applies to network integration. Hospitals often have complex environments containing many generations of technology, specialized protocols, and interconnected clinical systems. A connected device could potentially become an entry point into a larger environment if segmentation or access controls are poorly configured. Consequently, penetration testers may need to evaluate not only whether the device can be compromised but also what an attacker could potentially reach after compromising it.
Reporting Must Connect Technical Findings to Real-World Risk
The final report is another area where medical device penetration testing differs from ordinary IT assessments. A useful report should explain the technical vulnerability, how it was discovered, how it could be exploited, which security properties are affected, and what remediation steps are available. For medical devices, however, the report should also provide enough context for risk-management and engineering teams to understand the possible implications for the device’s intended function.
A vulnerability that permits unauthorized access to non-sensitive diagnostic information may require a different response from a weakness that could alter a critical device setting. Severity should therefore be considered alongside exploitability, exposure, affected assets, compensating controls, and potential safety or clinical consequences. Clear evidence, reproducible findings, and practical remediation guidance allow development and security teams to address weaknesses without relying on vague recommendations.
Documentation is particularly valuable in regulated environments. Manufacturers may need to demonstrate how cybersecurity risks were identified, assessed, mitigated, and monitored over time. Penetration testing results can become one component of that evidence when properly integrated into the broader cybersecurity process. Retesting after remediation is also important because a patch may address one vulnerability while introducing compatibility issues or leaving a related attack path unresolved.
Building Security Into the Medical Device Lifecycle
The strongest medical device security programs do not wait until a product is nearly ready for market before testing its defenses. Security can be incorporated from early architectural planning through development, verification, validation, deployment, maintenance, and eventual retirement. This lifecycle approach makes it easier to identify fundamental design weaknesses before they become expensive or difficult to correct.
Penetration testing is particularly valuable when it is treated as one part of continuous risk management rather than a single compliance exercise. Threats evolve, software changes, new vulnerabilities are disclosed, and devices may remain deployed for many years. Periodic reassessment can therefore provide information that a one-time test cannot. Manufacturers should also have processes for vulnerability disclosure, incident response, security updates, and postmarket monitoring.
The goal is to create devices that remain dependable in the environments where they are actually used. Security should support the device’s clinical purpose rather than becoming an isolated technical requirement. When engineers, security professionals, quality teams, regulatory specialists, and clinical stakeholders work together, testing can produce more meaningful results and help manufacturers address vulnerabilities before they become operational problems.
Conclusion
Penetration testing medical devices requires considerably more than applying a conventional IT checklist to a piece of connected hardware. Testers must understand the device’s architecture, clinical purpose, interfaces, dependencies, regulatory environment, and potential safety implications. They must also balance rigorous security assessment with carefully controlled testing practices that protect device functionality and patient safety.
The most effective approach is therefore one that combines technical depth with clinical and regulatory awareness. Penetration testing should work alongside threat modeling, secure development practices, vulnerability management, software analysis, risk assessment, and postmarket monitoring. When these activities are integrated throughout the product lifecycle, manufacturers gain a clearer understanding of how their devices could be attacked and, more importantly, how those attacks could affect the people and systems that depend on them.